Updated:
Biometric systems compare a measured characteristic, such as a fingerprint or face, with a reference representation. They can make an authentication step more convenient, but the comparison is not an infallible identity decision. A sound deployment considers where matching happens, what data is retained and how people recover access when the check cannot be used.
Enlarge illustration →
Verification is a comparison with limits
Verification generally asks whether a presented sample matches an enrolled reference for a claimed identity. Identification searches across a set of references to find a possible identity. These are different tasks with different exposure and performance considerations. Decide which task is actually necessary before selecting a product.
Biometric matching uses thresholds and can make errors. False matches and false non-matches depend on the system, sample quality and operating conditions. A result measured in one evaluation should not be assumed to describe every device, population or environment. Test the intended use rather than relying on an unqualified accuracy percentage.
Distinguish local unlock from central biometric storage
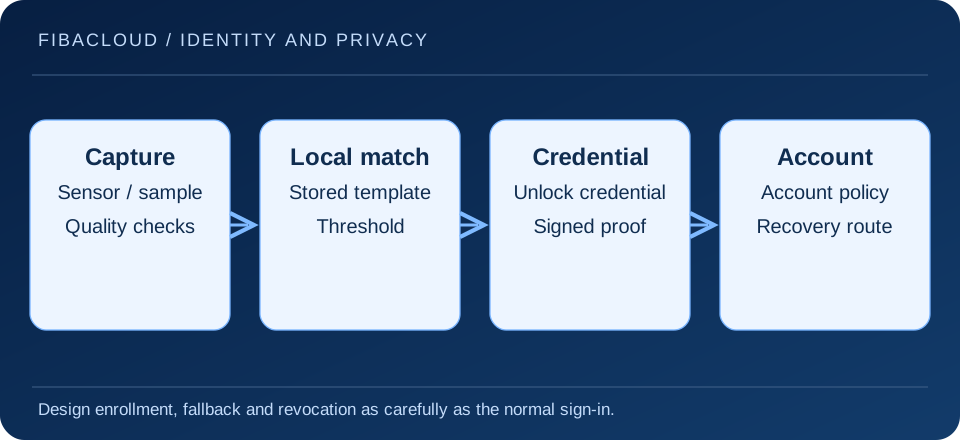
A device can use a local biometric check to authorize use of a cryptographic authenticator. In a suitable WebAuthn design, the service verifies a public-key assertion rather than receiving the raw fingerprint or face sample. This is different from a service collecting and matching biometric templates centrally.
Biometrics are not secret values in the same sense as a password. NIST authentication guidance treats their use within defined authenticator requirements rather than as an unrestricted standalone replacement for every factor. A passkey can use local verification methods other than biometrics, such as a device PIN, depending on the authenticator and policy.
Enrollment establishes the reference
A precise matcher cannot correct enrollment of the wrong person or the wrong account association. Decide how initial identity is established, who can enroll a new device and whether another factor or administrative review is required. Record security-relevant enrollment events without retaining unnecessary sensitive content.
Consider presentation attacks, such as an attempt to present a fabricated sample, and the product’s defenses against them. Sensor quality and liveness-related checks have limits. Treat them as controls to evaluate, not as proof that impersonation has become impossible.
Provide secure and usable recovery
People can lose a device or be unable to use a sensor because of injury, lighting, accessibility needs or device failure. Recovery must be available without creating a much weaker route into the account. Define alternative authenticators, identity checks and revocation procedures before enrollment begins.
A help desk process deserves the same scrutiny as the normal sign-in. An attacker may target recovery precisely because the biometric path is difficult. Staff need clear authority boundaries and records, while legitimate users need a route that does not depend on a single unavailable device.
Minimize privacy exposure
- Document which samples, templates and event records are collected and where they are processed.
- Collect only what the chosen authentication design requires.
- Limit access and retention, including copies in diagnostics and support exports.
- Explain the purpose, alternatives and relevant deletion or revocation process to users.
- Review applicable legal requirements before deployment in the intended jurisdiction.
A template compromise is not handled exactly like resetting a password. The underlying characteristic is difficult to change, although the technical impact depends on the template and matching design. Reduce unnecessary central collection and understand the vendor’s protection and recovery model.
Judge the complete access system
Evaluate enrollment, everyday verification, fallback, device loss and account recovery together. Measure usability and failure cases as well as attack resistance. The goal is a dependable access process with appropriate privacy controls, not simply a more impressive sign-in screen.
Frequently asked questions
- Does a website need my fingerprint to support biometric sign-in?
-
Not necessarily. A local authenticator can use biometrics to authorize a cryptographic operation while the service receives a public-key assertion. The actual design must be verified.
- Are biometrics impossible to bypass or misuse?
-
No. Matching, enrollment, devices and recovery can all introduce weaknesses. Evaluate the whole authentication process and its operating conditions.
Your next step
Connect authentication decisions to the cloud security plan. Inventory administrative identities, authenticators and recovery owners before introducing a new biometric access method.