Updated:
Cloud security is not completed by enabling one product. Identities, network access, applications, data and recovery processes need to work together. Start by identifying what must be protected, which events would affect the business and who is responsible for operating each control.
Enlarge illustration →
Establish scope and ownership
Inventory servers, data stores, domains, administrative accounts and external service connections. Distinguish production, testing and personal experiments. Patching and access reviews are easily missed when a resource has no owner. Important components should have both technical ownership and a clear business purpose.
A provider operating physical infrastructure does not automatically manage the customer’s operating system or application. Managed products change the boundary within their stated scope. Assign patching, firewall maintenance, backups, log review and incident response individually instead of treating security as a single transferred responsibility.
Limit identity and privilege
Use suitable multifactor authentication for administration and avoid shared accounts. Separate everyday permissions from exceptional administrative access. Record where API keys are used, who renews them and how they can be revoked. A secret without an owner can remain active long after its original purpose has disappeared.
When a staff member or supplier leaves, review accounts, keys and connection paths together. Disabling one login may not invalidate automation credentials. Make access review a routine operating activity rather than something performed only after an incident. Remove unused access to reduce unnecessary exposure.
Combine network and application controls
Do not expose management ports more broadly than needed. Define the resources and routes that require access. Network rules do not replace application authorization. Public applications still need sound session handling, input processing, dependency updates and secret management.
Before tightening a rule, identify the application’s actual dependencies and prepare a test and rollback route. Verify both that intended access works and that unnecessary access is blocked. A successful connection alone does not demonstrate that a boundary is correctly enforced.
Protect data and prove recovery
Classify information by sensitivity and business value. Decide how it is protected in transit and at rest, who can use encryption keys and how long it is retained. Encryption does not prevent an authorized account from accidentally deleting records. Backups and restricted permissions address different risks.
Define the failure a backup is intended to survive. Copies in the same account or storage environment may be affected by one event. A restoration exercise should check readable data, consistency and application operation. Agree acceptable data loss and service recovery time with the business, not only with the infrastructure team.
Make monitoring actionable
- Select meaningful events such as administrative logins, privilege changes and critical application errors.
- Assign someone to review each alert and define when intervention is required.
- Keep clocks consistent and apply suitable retention and access restrictions to records.
- Document credential revocation, isolation, evidence preservation and recovery steps for an incident.
- Reassess controls after changes rather than treating an old test as permanent assurance.
For a small team, a manageable set of controls that operates reliably is a useful starting point. Prioritize critical identities, backups and external access, with a record of what was checked. Expanding a toolset without assigning response ownership can create more noise without improving the team’s ability to act.
Review the plan when applications, staff responsibilities or data use change. Security decisions should follow the current environment rather than remain tied to assumptions made during its first deployment.
Frequently asked questions
- Does the cloud provider take all security responsibility?
-
Only within the service’s defined scope. Customer data, user permissions and applications usually retain customer responsibilities that should be explicitly assigned.
- Is seeing a backup file enough?
-
No. Restoration, data consistency and application operation need to be checked. A file listing alone does not demonstrate recoverability.
Your next step
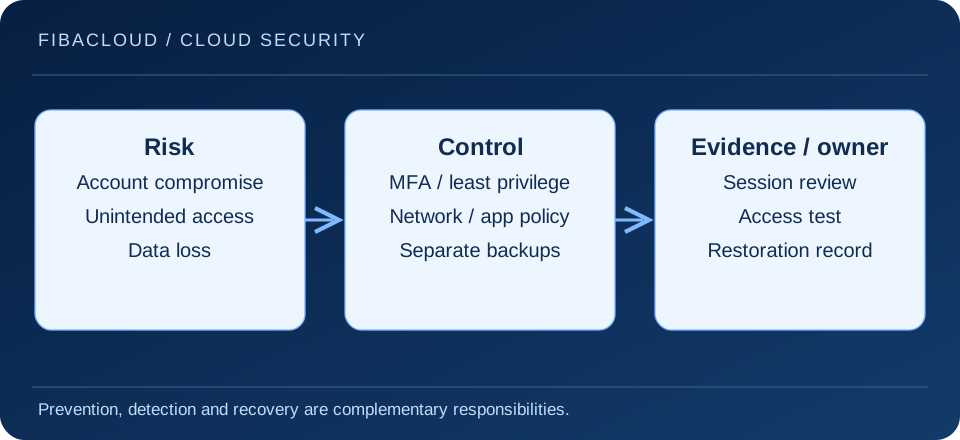
Connect the VPN access boundary and backup plan to this process. Give each important risk an owner, a control and a verification record.