Updated:
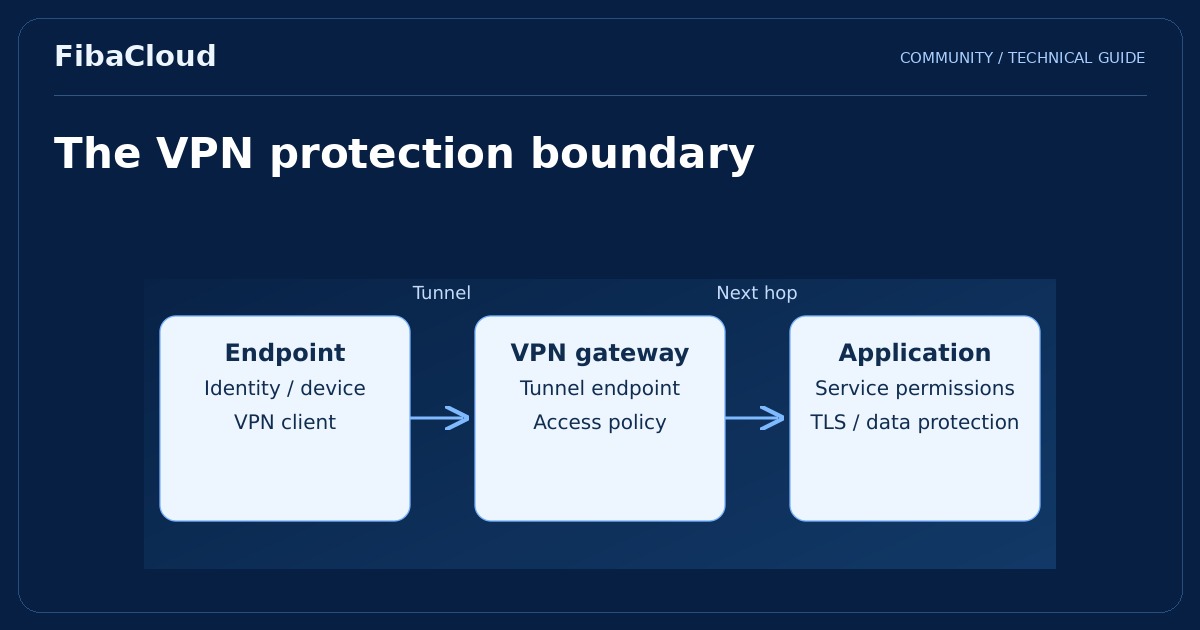
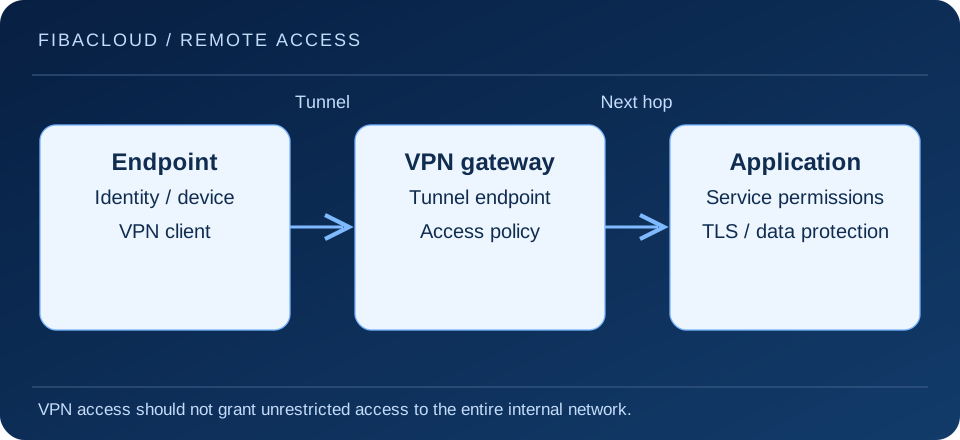
A cloud VPN connects users or networks to cloud resources through a VPN tunnel. The tunnel protects specified traffic between its endpoints; it does not automatically secure every action on a device or every part of an application. A sound design begins by identifying exactly where that protected path starts and ends.
Enlarge illustration →
Remote access and site-to-site connectivity
A remote access VPN connects a user’s device to authorized resources. A site-to-site VPN connects networks, such as an office network and a cloud network. User identity and device security are central in the first model; address ranges, routing and gateway compatibility are particularly important in the second.
Both models can be used together without sharing identical permissions. An employee accessing a management interface and an application connecting to a database have different needs. Define access by person, service and destination instead of using the tunnel as a universal key to the internal network.
Understand which traffic is protected
Encryption covers the specified traffic between tunnel endpoints. Traffic leaving the tunnel may still need application protection such as TLS. A compromised device, an overprivileged account or an application vulnerability does not disappear when a VPN connects. Maintain identity, endpoint and application controls separately.
With split tunneling, selected destinations use the VPN while other traffic uses the device’s existing connection. A full tunnel routes a broader set of traffic through the gateway. These choices affect DNS, bandwidth, monitoring and access policy. Verify the route that real application traffic takes rather than inferring it from the client’s connection status.
Plan addressing and routing first
Overlapping private address ranges can prevent useful connectivity even when the tunnel appears healthy. Routing, return paths, DNS resolution and firewall rules must work together. A connected tunnel proves less than a successful authorized application transaction.
MTU and fragmentation can cause selective failures: a small connectivity check may pass while a larger transfer stalls. Before assuming insufficient bandwidth, inspect the destination service, packet size and both directions of the flow. Make changes with records and a recovery path available.
Apply enterprise access controls
- Use individual or service identities instead of shared accounts, with suitable multifactor authentication.
- Allow only required subnets and ports, assessing management resources separately.
- Define certificate or key distribution, renewal and revocation procedures.
- Maintain gateways and clients on supported releases and schedule controlled updates.
- Retain necessary session and security events without collecting secrets or unnecessary personal data.
When an employee leaves, changing a password may not revoke every credential. Certificates, keys and active sessions should be handled according to the product’s capabilities. Periodic access review matters as much as initial configuration.
Test useful access and failure behavior
Verify that an authorized user can reach the intended service, cannot reach prohibited destinations and receives the expected DNS response. Document gateway maintenance, certificate expiry and office connectivity loss procedures. If another tunnel or gateway is present, exercise failover at the application level instead of assuming that a spare component proves resilience.
Keep a connection inventory that identifies each tunnel’s owner, peer, permitted networks and business purpose. This makes troubleshooting more focused and helps the team recognize obsolete access when applications move or office networks change.
Frequently asked questions
- Does a VPN provide complete anonymity?
-
No. Applications, services and network operators can still observe various connection or account details. Visibility depends on the architecture and purpose of the VPN.
- Is HTTPS still needed when a VPN is used?
-
Usually yes. HTTPS protects an application connection between its own endpoints; the VPN tunnel can end at a different point.
Your next step
Use the firewall guide to define access boundaries and the cloud security guide for identity and recovery ownership. Confirm any FibaCloud network capability against the service’s actual scope.