Updated:
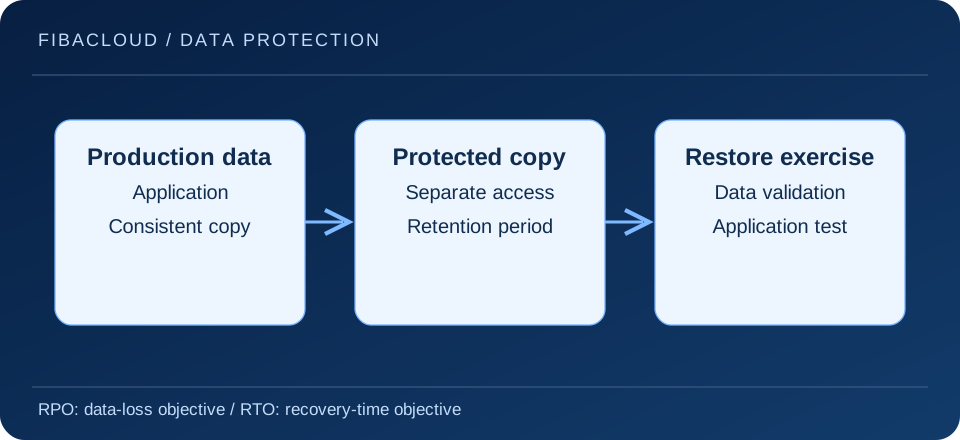
Cloud backup stores recoverable copies of data in a cloud service. Its value depends on more than creating a copy: the right information must be protected, a suitable recovery point must remain available, and the application must be able to run after restoration. Backup is therefore an operational process as well as a storage choice.
Enlarge illustration →
Define the complete recovery scope
An application may need more than uploaded files. Databases, configuration, certificates, application versions and a way to retrieve required secrets can all matter. Putting secrets into an unprotected archive introduces another risk. Plan secure key storage and how authorized staff will obtain the keys during recovery.
Record who owns each dataset, how long it must be retained and whether it can be recreated. A database containing customer transactions has a different recovery priority from a disposable cache. This distinction helps control backup size without leaving critical information outside the plan.
Backups, snapshots and replicas differ
A snapshot can help return storage to a particular point in time. If it remains on the same storage system, it may share that system’s failure domain. Copying the files of a running database does not always create an application-consistent backup. Use the database’s supported backup method and include any logs required for the intended recovery process.
Replication sends changes to another system, potentially including accidental deletion or corruption. Having a replica does not necessarily provide a clean historical recovery point. Backup design should account for retained versions, separate access controls and appropriate retention. The techniques complement one another; naming one does not satisfy the requirements of the others.
Translate business needs into recovery objectives
The recovery point objective, or RPO, describes acceptable data loss in time. The recovery time objective, or RTO, describes the target time to restore service. Define both around business impact. A backup schedule alone does not guarantee an RPO: failed jobs or missing log transfers can change what is actually recoverable.
Include provisioning, data retrieval, decryption, application startup and validation in the recovery-time estimate. Low-cost archive storage is not necessarily quick to retrieve. Check the selected storage class, retrieval conditions and network capacity against the actual service terms. A restore rehearsal gives more useful evidence than a storage-capacity figure alone.
Protect access to the copies
Using the same credentials to operate production and delete its backups creates a shared point of failure. Separate permissions, use strong authentication and monitor changes to retention or deletion controls. Immutable retention and object-lock features are effective only when the service supports them and they are configured appropriately. They should not be assumed to exist by default in every object storage service.
Encryption does not replace access management. Lost encryption keys can make a valid copy unusable, while unauthorized key access can undermine confidentiality. Document who can perform a recovery and how that person obtains the required access during an incident, including when the normal production environment is unavailable.
Run a meaningful restoration exercise
- Choose an isolated environment and a specific recovery point.
- Restore the required files, database and application dependencies.
- Validate data integrity, authentication and representative business transactions.
- Record elapsed time and missing steps, then compare the result with the objectives.
- Remove test data appropriately and update the operational procedure.
A last-successful-job timestamp is useful monitoring information, but it is not a substitute for this exercise. Revisit the process when the application, data volume or infrastructure changes. A dependable plan connects the business requirement to an owner, a recoverable copy and a repeatable validation procedure.
Frequently asked questions
- Is one backup per day sufficient?
-
That depends on acceptable data loss. Important activity during the day may require more frequent copies or an application-supported log-based recovery method.
- Does a successful backup notification prove recovery works?
-
No. Restoration, data integrity and application behavior must be validated separately.
Your next step
Read the replication guide to compare the approaches. When considering cloud backups, check retention, coverage and restoration conditions for your application.